Chad Raduege on Why Biopharma Cybersecurity Is National Security
What you’ll learn
- Why a retired Air Force general treats biopharma cybersecurity as a national security question
- How ransomware differs from espionage by advanced persistent threats that wait inside a network for years
- Who is accountable when a 40-person biotech with no CISO keeps its data with CROs, manufacturers and cloud vendors
- What an adversary could learn from a venture firm’s due diligence files that it could not learn from one company
- How crown jewel analysis and information sharing change what a small company protects first
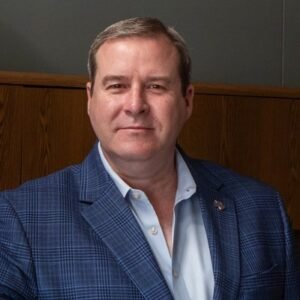
Chad Raduege treats biopharma cybersecurity as a national security question, and he has the background to make that case. He retired from the U.S. Air Force in 2023 as a brigadier general after 29 years in communications, IT and cyber operations, including command of the White House Communications Agency and a final posting as Director of C4/Cyber and Chief Information Officer for U.S. European Command. Today he is President of Cyber, Data & Communications at Elara Nova.
Lori Ellis opened with the question he was trained to answer: when someone assesses targets, where does biopharma fall?
Why the label matters less than the data
Raduege declined the premise first. “I would push back a little bit on trying to put pharma or bio into a specific category,” he said. Healthcare is one of the sectors the federal government designates as critical infrastructure, but the category is not what an adversary is weighing. The questions he would ask instead are about the asset itself: “What type of data is available here? What type of information is being used and how does it all come together?” Then who holds it, who can reach it, and why a foreign adversary would want it.
Run biopharma through those questions and the answer comes back large. Biological data built on decades of research and billions of dollars. Clinical trial results. Manufacturing capacity, which the COVID response showed the whole country depends on. Emerging technology, heavy investment, and a concentration of scientific talent. Put together, he said, “this is really starting to hint at national security implications.” His conclusion was plain: this is something a nation state would be interested in, not just a hacker.
Ransomware and espionage are different threats
Lori Ellis pressed him to separate the attackers. Raduege described ransomware operators as thieves: they break in, hold data for ransom and ask for money. Espionage worries him more. The military term is advanced persistent threat, and it describes state actors who behave the opposite way a criminal does. They avoid being noticed, and they are not after quick money. They want “a foothold in there where they can study for years and then activate at a time and place of need.”
He also said adversaries look for what is easy to get into, the low-hanging fruit, and that healthcare is often associated with that. An earlier guest on this show put the weight elsewhere, when a litigator argued that small biotechs draw attention because they hold the newest science. Both views put the smaller companies squarely in the frame.
The 40-person biotech with no CISO
Lori Ellis described a company many listeners will recognize: forty people, no security staff, trial data held by a contract research organization, process data by a contract manufacturer, and everything else by cloud vendors. Who is accountable, and what is the first honest move for a company that cannot hire a chief information security officer?
Raduege answered that the problem starts before the hire. “I think it goes beyond just hiring the CISO. This really becomes a cultural thing for an organization as a whole.” For a young founder building around an idea and a team, security tends to sit low on the list. Meanwhile “the security perimeter now extends beyond just your company,” into cloud providers, commercial internet service providers, suppliers and payment flows.
On accountability he drew on command. Infrastructure can be distributed and so can tasks, but someone has to accept the risk: “You have to accept the risk and really the CEO is responsible for pulling that together.” A CEO does that through the leadership team and the board, and by asking where the data is stored and who can reach it. If a company is not asking those questions, he said, it is in trouble.
What an adversary learns from a diligence file
Lori Ellis raised a real incident: Insight Partners disclosed that data on its funds, its portfolio companies and its limited partners was stolen in an attack it disclosed in 2025. What can an adversary do with a firm’s deal flow that it cannot do with one company’s network?
Raduege called due diligence the point where national security starts to apply. A company protecting itself protects one company. An investor running diligence assembles the competitive landscape, the rival companies it evaluated, and a frank assessment of where each is strong and weak, including which forty-person companies have no security leadership. “When I look at the venture capitalists, I say, holy cow, now they have insight into the industry as a whole.” If that package is not protected, a nation-state actor gets a map of where the best science and the clinical data sit, across companies that compete with one another.
Asked who should answer for a breach, he pushed against making it one person’s fault, usually the security or IT chief. The fairer question is whether that person warned the board, asked for funding or advised against a particular cloud setup. “I don’t think it’s one individual that tends to or should be held accountable for this unless you’re talking about the CEO.”
Crown jewels, and why you cannot protect everything
The CEO’s first question, in his view, is the military one: what are the crown jewels? What data is most critical to the mission, where does it reside, who has access, and what could someone do with it?
He explained why the exercise matters with his old network of 750,000 endpoints. Protecting all of them equally is not realistic, because “defense has to be right all of the time. The offense or the hacker just has to be right once and then they’re in.” The Air Force answer was to identify the most critical systems and data, then build dedicated teams around them, an initiative it called Mission Defense Teams. The lesson he took: protecting everything is a losing battle, and protecting a few things well is achievable.
Is someone mapping the industry?
Lori Ellis listed three incidents from this summer: Amgen in July, Boston Scientific in August and McKesson at the end of August. Did the sequence tell him anything a single incident would not?
Raduege read it as a trend. The companies saw different effects, from data exposure to operational disruption, reached by different routes: “three different companies, three different adversary tactics to get in.” To an offensive cyber operator, he said, that looks like mapping, probing an industry to see where defenses are strong and weak. The public record is still incomplete on how each intrusion happened, and McKesson’s was claimed by a criminal extortion group, so this is his own read of the pattern. Lori Ellis added that the pressure has moved from health systems to vendors, and that global clinical trials widen the exposure further, since networks do not stop at national borders.
Build it in, and stop casting stones
His advice for small companies and their investors came back to the line that opens the episode. “Often first to market means that you take shortcuts. And if you’re taking shortcuts on the cybersecurity side, that’s a danger, danger alert.” A company that ships with holes in its network may have intruders already in place. His phrase for the alternative: build it in, don’t strap it on.
He closed with a request of the industry. After a breach, boards and Congress often look for someone to hold accountable right away. Raduege pointed instead to information sharing and analysis centers, the sector groups where companies share what happened so the next one is better prepared, and said that “casting stones at the glass house is not a productive environment.” Lori Ellis compared it to drug development, where a failed trial teaches the whole field. She would like cybersecurity to learn the same way.
For a related conversation, a biotech security chief and a litigator explained what nation states want from smaller companies, and our explainer covers what nation-state hackers actually want from a biotech.
Defense has to be right all of the time. The offense or the hacker just has to be right once and then they’re in.
Key takeaways
- Start with the data, not the label. Raduege asks what data a company holds, who can reach it, and why an adversary would want it before asking which sector it belongs to.
- Biopharma adds up to a strategic target. Research data, clinical trials, manufacturing capacity, emerging technology and scientific talent together carry national security weight.
- Ransomware and espionage are different threats. Ransomware operators want money quickly. Advanced persistent threats want a quiet foothold they can use years later.
- The perimeter has moved. Cloud providers, internet service providers, suppliers and payment flows are now part of a company’s attack surface.
- The CEO accepts the risk. Tasks and infrastructure can be distributed, but someone has to own the risk calculus, and Raduege places that with the CEO.
- Diligence files are an intelligence prize. A venture firm’s package on a sector shows where the best science, the clinical data and the weak defenses sit across competitors.
- Protect the crown jewels first. Defending every endpoint equally is a losing battle. Identifying the most critical data and systems makes protection achievable.
- Build security in from the start. A company that rushes to market with holes in its network may already have intruders in place.
- Share what happened. Raduege points to information sharing and analysis centers as a better response to breaches than public blame.
Key Questions, Answered
Where does biopharma sit on a nation-state target list?
I would push back a little bit on trying to put pharma or bio into a specific category.
Raduege resists sector labels and starts from the data a company holds.
Why would a nation state care about biopharma data?
This is really starting to hint at national security implications... So I view it as something that a nation state would be interested in, not just a hacker.
Research, trial data, manufacturing and talent add up to national security weight.
How is ransomware different from espionage?
When I hear the word ransomware, I think of thieves that are really just trying to break in, hold your data for ransom, ask for some money... When I start hearing the word espionage, that’s where I get a little more concerned.
Ransomware is theft for money; espionage is where his concern rises.
What does an advanced persistent threat want?
They’re not interested in making themselves known in your network. They’re not necessarily interested in making short-term money. They’re interested in getting into your networks and putting a foothold in there where they can study for years and then activate at a time and place of need.
A quiet foothold inside a network that can be used years later.
What should a 40-person biotech with no CISO do first?
I think it goes beyond just hiring the CISO. This really becomes a cultural thing for an organization as a whole.
Treat security as company culture before treating it as a hire.
Who is accountable for cybersecurity at a biotech?
You have to accept the risk and really the CEO is responsible for pulling that together.
Infrastructure can be distributed; the CEO makes the risk decision.
What can an adversary learn from a venture firm’s due diligence files?
When I look at the venture capitalists, I say, holy cow, now they have insight into the industry as a whole.
Diligence packages map a whole sector, including the companies an investor evaluated.
Who should be blamed after a breach?
I don’t think it’s one individual that tends to or should be held accountable for this unless you’re talking about the CEO.
Raduege argues against making one security leader the scapegoat.
Why protect the crown jewels first?
Really it was an acknowledgement that trying to protect everything is a losing battle. But can you protect this one thing or these couple of things? Yeah, you can do a better job with that.
Prioritizing the most critical data makes defense achievable.
Do the Amgen, Boston Scientific and McKesson incidents form a pattern?
To me, it creates a trend of there is mapping that is going on.
He reads three incidents with different tactics as a sign of mapping.
What should a startup racing to market do about cybersecurity?
You really need to build cybersecurity in from the beginning. We talk about building it in and not strapping it on.
Build security in from the beginning instead of adding it later.
Why should life sciences companies share breach information?
The whole idea is to create an ecosystem around this information sharing idea where we grow stronger together. You were hacked today, we’re probably gonna be hacked tomorrow.
Sector information sharing helps the next company prepare.
Resources
- Elara Nova Space and technology consultancy where Chad Raduege is President of Cyber, Data & Communications.
- Chad Raduege, Elara Nova profile Official biography, including his Air Force career and current roles.
- Insight Partners statement on its 2025 cyber incident The firm’s disclosure of the January 2025 incident discussed in the episode.
- Amgen cybersecurity event Amgen’s notice on unauthorized access to data in third-party cloud environments, 2026.
- Boston Scientific update on its cybersecurity incident Company update on the incident detected August 25, 2026.
- McKesson discloses breach (BleepingComputer) Reporting on McKesson’s August 2026 disclosure and the extortion group’s claim.
- CISA: critical infrastructure sectors The 16 sectors, including healthcare and public health, that Raduege refers to.
- Space ISAC The information sharing and analysis center for the space sector that Raduege describes.
- Health-ISAC The information sharing and analysis center for healthcare. Our addition for readers in the sector; not named in the episode.
Need the life-sciences signal but short on time?
Get the free quarterly briefing: every guest from the quarter, in one sitting. What decides whether a therapy reaches a patient, gets funded, and can be trusted.